



Cybersecurity is becoming a critical priority as businesses, governments, and individuals depend more heavily on digital systems. Online transactions, cloud-based applications, connected devices, and remote working environments have expanded the ways people use technology, but they have also created new opportunities for cybercriminals.
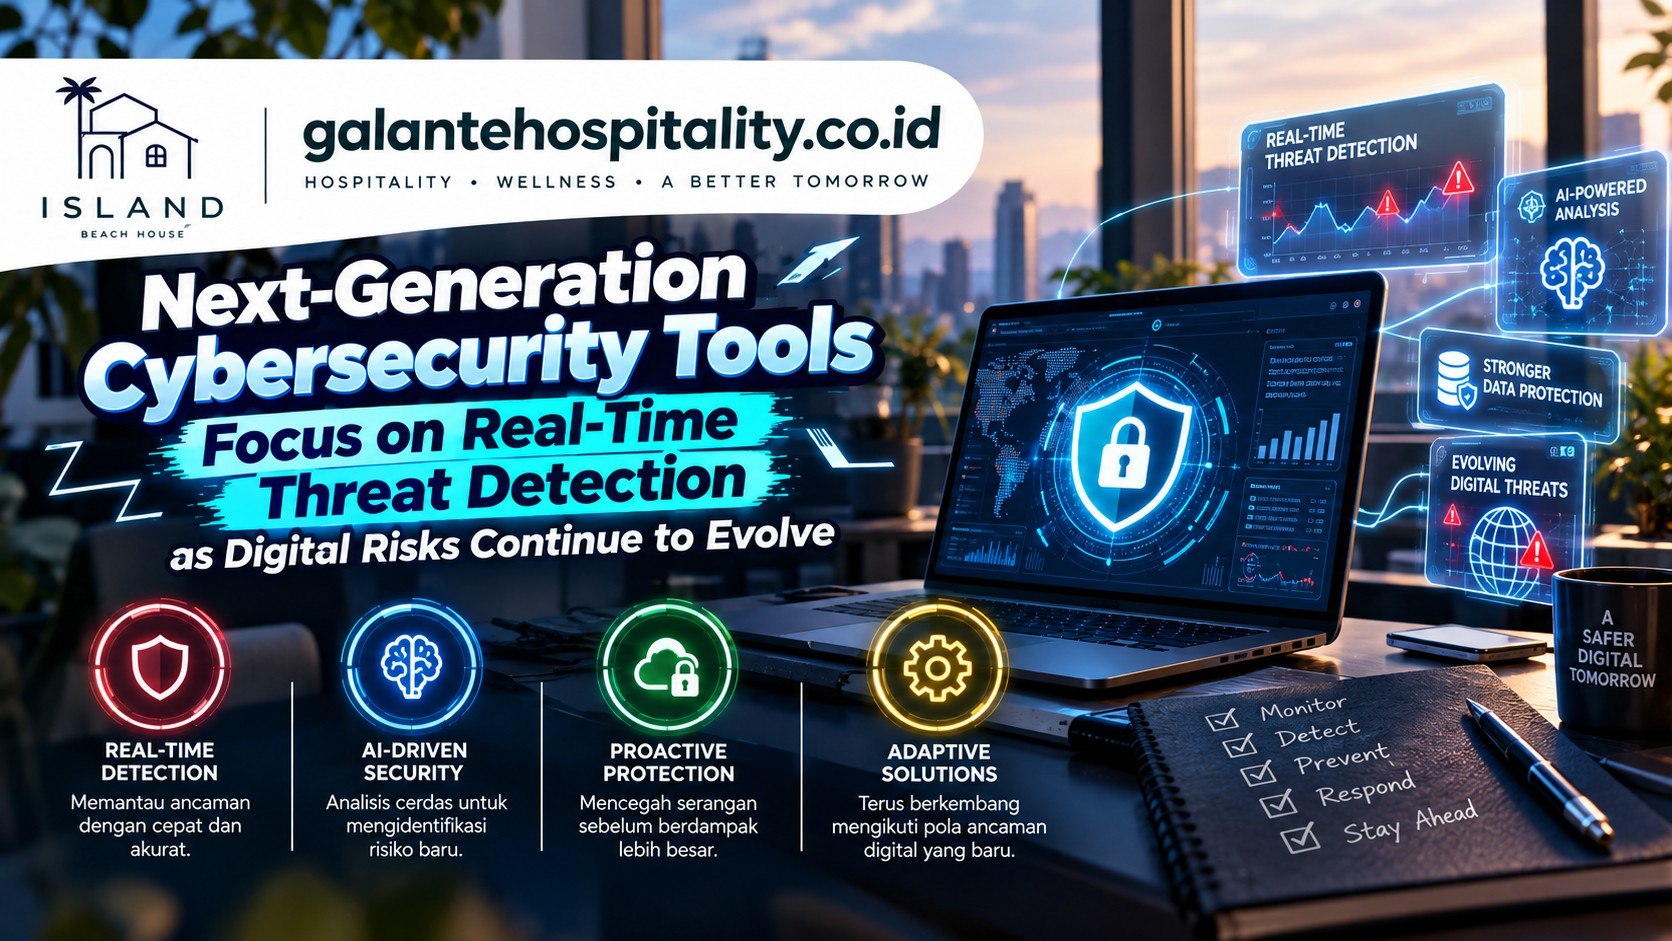
To respond to these challenges, cybersecurity providers are developing and improving tools that identify suspicious activity, analyze potential threats, and help organizations respond more quickly to security incidents. Real-time threat detection is an important part of this approach because it can help security teams recognize unusual behavior before a problem causes widespread damage.
However, effective cybersecurity requires more than sophisticated software. Organizations also need strong security policies, trained employees, and reliable procedures for responding to incidents.
Why Real-Time Threat Detection Matters
Traditional security systems often rely on known threat signatures, predefined rules, and periodic monitoring. These methods remain useful, particularly for identifying familiar forms of malicious software. However, attackers may change their techniques to avoid detection or exploit weaknesses that security teams have not previously encountered.
Real-time monitoring adds another layer of protection by examining activity as it occurs. Security systems can look for unusual login patterns, unexpected data transfers, suspicious application behavior, and other indicators that may require investigation.
For example, if an account suddenly attempts to access sensitive files from an unfamiliar location or performs an unusual number of actions within a short period, a security platform may flag the activity for review.
Not every unusual event represents an attack. Employees may travel, change devices, or perform legitimate tasks outside their normal routines. Security teams therefore need to evaluate alerts carefully to avoid unnecessary disruption.
Artificial Intelligence Supports Threat Analysis
Artificial intelligence and machine learning can help security systems process large amounts of information and identify patterns that would be difficult to detect manually.
These technologies can assist with analyzing network traffic, prioritizing alerts, identifying potentially compromised accounts, and summarizing information for security analysts. By organizing large volumes of security data, AI-supported tools may help teams focus their attention on the incidents that require the most urgent investigation.
Automation can also reduce the time needed to perform certain routine tasks. Depending on the system and its configuration, a security platform may temporarily isolate a device, disable a suspicious session, or request additional authentication when specific conditions are met.
Nevertheless, AI is not a complete solution to cybersecurity threats. Automated systems can produce false alarms, overlook sophisticated attacks, or misinterpret legitimate behavior. Human oversight remains important, especially when automated responses could interrupt essential business operations.
Cloud Security Requires a Broader Approach
Many organizations now store information and operate applications across cloud services, company networks, and employee devices. This distributed environment can make it harder to maintain consistent security standards.
A strong security strategy should account for user identities, device health, access permissions, data protection, and application activity. Organizations should also apply the principle of least privilege, which means users receive only the access necessary to perform their responsibilities.
Multi-factor authentication can provide an additional layer of protection by requiring another verification method beyond a password. Regular software updates, secure configuration, encrypted data storage, and tested backups also help reduce exposure to common threats.
Businesses should review their security arrangements whenever they introduce new applications or connect external services to internal systems.
Employees Remain an Important Part of Cybersecurity
Technology alone cannot eliminate every risk. Phishing messages, fraudulent websites, social engineering, and stolen credentials continue to create opportunities for unauthorized access.
Employees should learn how to identify suspicious messages, verify unusual requests, and report potential security incidents promptly. Organizations can support this effort through practical training, clear reporting channels, and regular security exercises.
Security policies should encourage early reporting rather than create a culture in which employees are afraid to admit mistakes. Quick communication can help an organization investigate an incident before it becomes more serious.
Building a More Resilient Digital Environment
The future of cybersecurity will likely involve closer integration between threat detection, identity management, automated response, and continuous monitoring. As digital risks evolve, organizations will need to review their defenses regularly rather than relying on a single security product.
Businesses should assess their most important assets, understand their potential vulnerabilities, and prioritize protections based on risk. They should also establish an incident response plan and test whether critical systems can be restored after an attack.
Real-time threat detection can improve visibility and help security teams respond more efficiently, but its effectiveness depends on the quality of the wider security strategy.
By combining appropriate technology, employee awareness, and consistent risk management, organizations can strengthen their defenses and build greater confidence in their digital operations.


